DigiCert X9 mTLS Certificate with Client Auth EKU
DigiCert X9 PKI for TLS is a certificate primarily intended for host-to-host communication (mTLS, API, internal services) outside of web browser environments. Its key advantage is support for Client Authentication EKU (typically combined with Server Authentication EKU) – precisely the usage that is gradually ending in the WebPKI world. X9 PKI is regulated by ASC X9 standards and ensures interoperability through a shared root of trust.
 Order
 Certificate comparison


OV - Organization Validation
client auth EKU
SAN (FQDN / IP)
issuance time

outside WebPKI
- Price £349
- Validity Multiple years
- Usage mTLS / API / host-to-host
- Trust standalone PKI (not webPKI)
- EKU Client Auth, Server Auth, or both
- Public key length 2,048 (3,072/4,096) bits
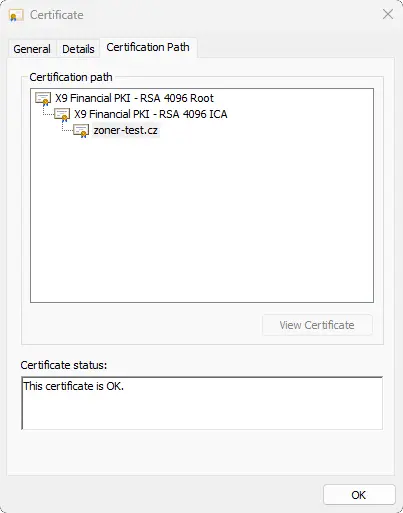
- Root / trust X9 Financial PKI - RSA 4096 Root
- Support for multiple domains up to 250 SAN
- Public key RSA and ECC
- Certificate re-issuance FREE
- Additional domains option YES
- Reissue / duplicates free (unlimited)
Recommended Uses for the Certificate
DigiCert X9 PKI for TLS is ideal wherever a TLS certificate is not primarily for the "web in the browser," but for system-to-system authentication. Typically, it's for mutual TLS (mTLS), API security, microservices communication, integration layers, and other host-to-host scenarios.
The main benefit of X9 PKI is the Client Authentication EKU in the certificate. In the common WebPKI environment, the use of public TLS certificates for client authentication is gradually ending, which complicates mTLS and internal PKI scenarios. X9 PKI provides a standardized alternative outside the browser ecosystem.
The certificate supports up to 250 SAN items per certificate (FQDN and/or IP addresses). Wildcard domains are not supported – only fully qualified DNS names and IP addresses can be included in the certificate.
Pricing Table for DigiCert X9 PKI for TLS Certificate
The DigiCert X9 PKI for TLS certificate supports up to 250 SAN items (FQDN and IP addresses). Wildcard domains cannot be used in the certificate.
One-Year
- Unlimited reissue and duplicates
- Client Auth EKU for mTLS
Extension
+ 1x SAN (FQDN or IP): £349.00
Multi-Year Order
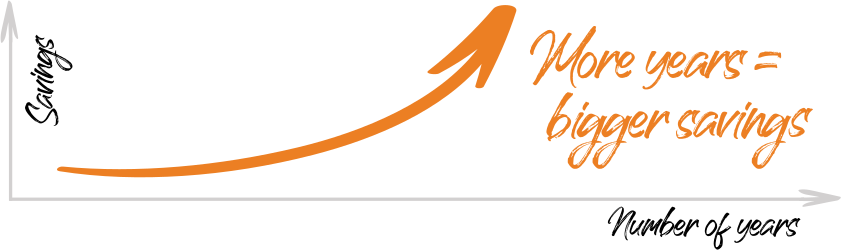
By ordering for multiple years, you save. You can order the certificate for up to 3 years. Every year you receive a consecutive one-year certificate.
- Less administration: one order, one payment.
- Higher savings with longer validity.
- You automatically receive the subsequent certificate.
Prices stated without VAT.
Use of Certificate Outside Web Browsers
DigiCert X9 PKI for TLS is designed for infrastructure where mutual authentication (mTLS) is key and control over how and where certificates are used is important – typically in internal networks, B2B integrations, and API communication.
Unlike "web" TLS certificates, the main goal is not visual indication in the browser, but machine/service identity, encryption, and interoperability within X9 PKI with independent certification policy.
If you are addressing the transition due to Client Authentication EKU restrictions in WebPKI, X9 PKI is the typical path to maintain the mTLS model long-term.
FAQ – Frequently Asked Questions About DigiCert X9 Certificates
If you need a standard TLS certificate for a public website (WebPKI, browser trust), choose standard DV/OV/EV certificates.
However, if you are dealing with mTLS, API communication, host-to-host connections, or communication between financial institutions, a DigiCert X9 certificate is a suitable choice.
These certificates:
- enable Client Authentication (EKU) – thus, mutual TLS verification,
- can be issued for a multi-year period,
- operate within a private trust between financial institutions, not as public WebPKI certificates.
If you're unsure, contact our customer support.
No. DigiCert X9 certificates only support specific FQDN and optionally IP addresses. Wildcard domains (e.g., *.domain.cz) are not supported.
No. DigiCert X9 certificates are not intended for public websites and are not part of the standard WebPKI trust in common browsers.
They are intended for a closed trust model between financial institutions, where trust is governed contractually and technically within the given ecosystem.
Yes. DigiCert X9 certificates support Extended Key Usage (EKU) for Client Authentication, which allows secure mTLS scenarios.
This type of client authentication is not commonly available with public WebPKI certificates today, which is one of the main reasons why X9 is suitable for banking and financial infrastructure.
Do you have questions?
Don't hesitate to contact our customer support, who will advise and help you.