DigiCert ONE
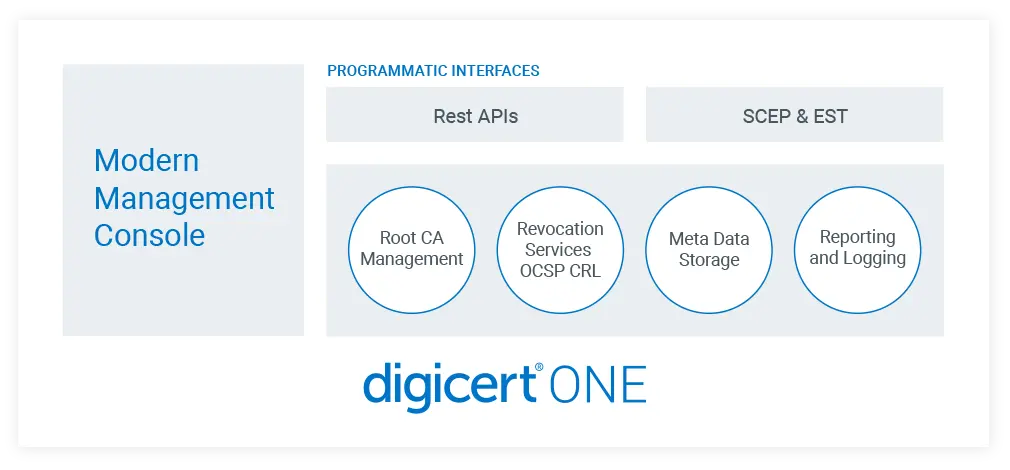
Let us introduce the most modern and versatile PKI platform in the world – DigiCert ONE. It consists of five components that cover all conceivable needs. A unified platform, modern architecture, and flexible deployment options. That's DigiCert ONE, and now you can use it too.
DigiCert ONE consists of these five components:
- DigiCert Trust Lifecycle Manager
- DigiCert Software Trust Manager
- DigiCert Document Trust Manager
- DigiCert CertCentral TLS Manager
- DigiCert IoT Trust Manager
You can use the individual components of DigiCert ONE together in one integrated platform or separately.
DigiCert Trust Lifecycle Manager
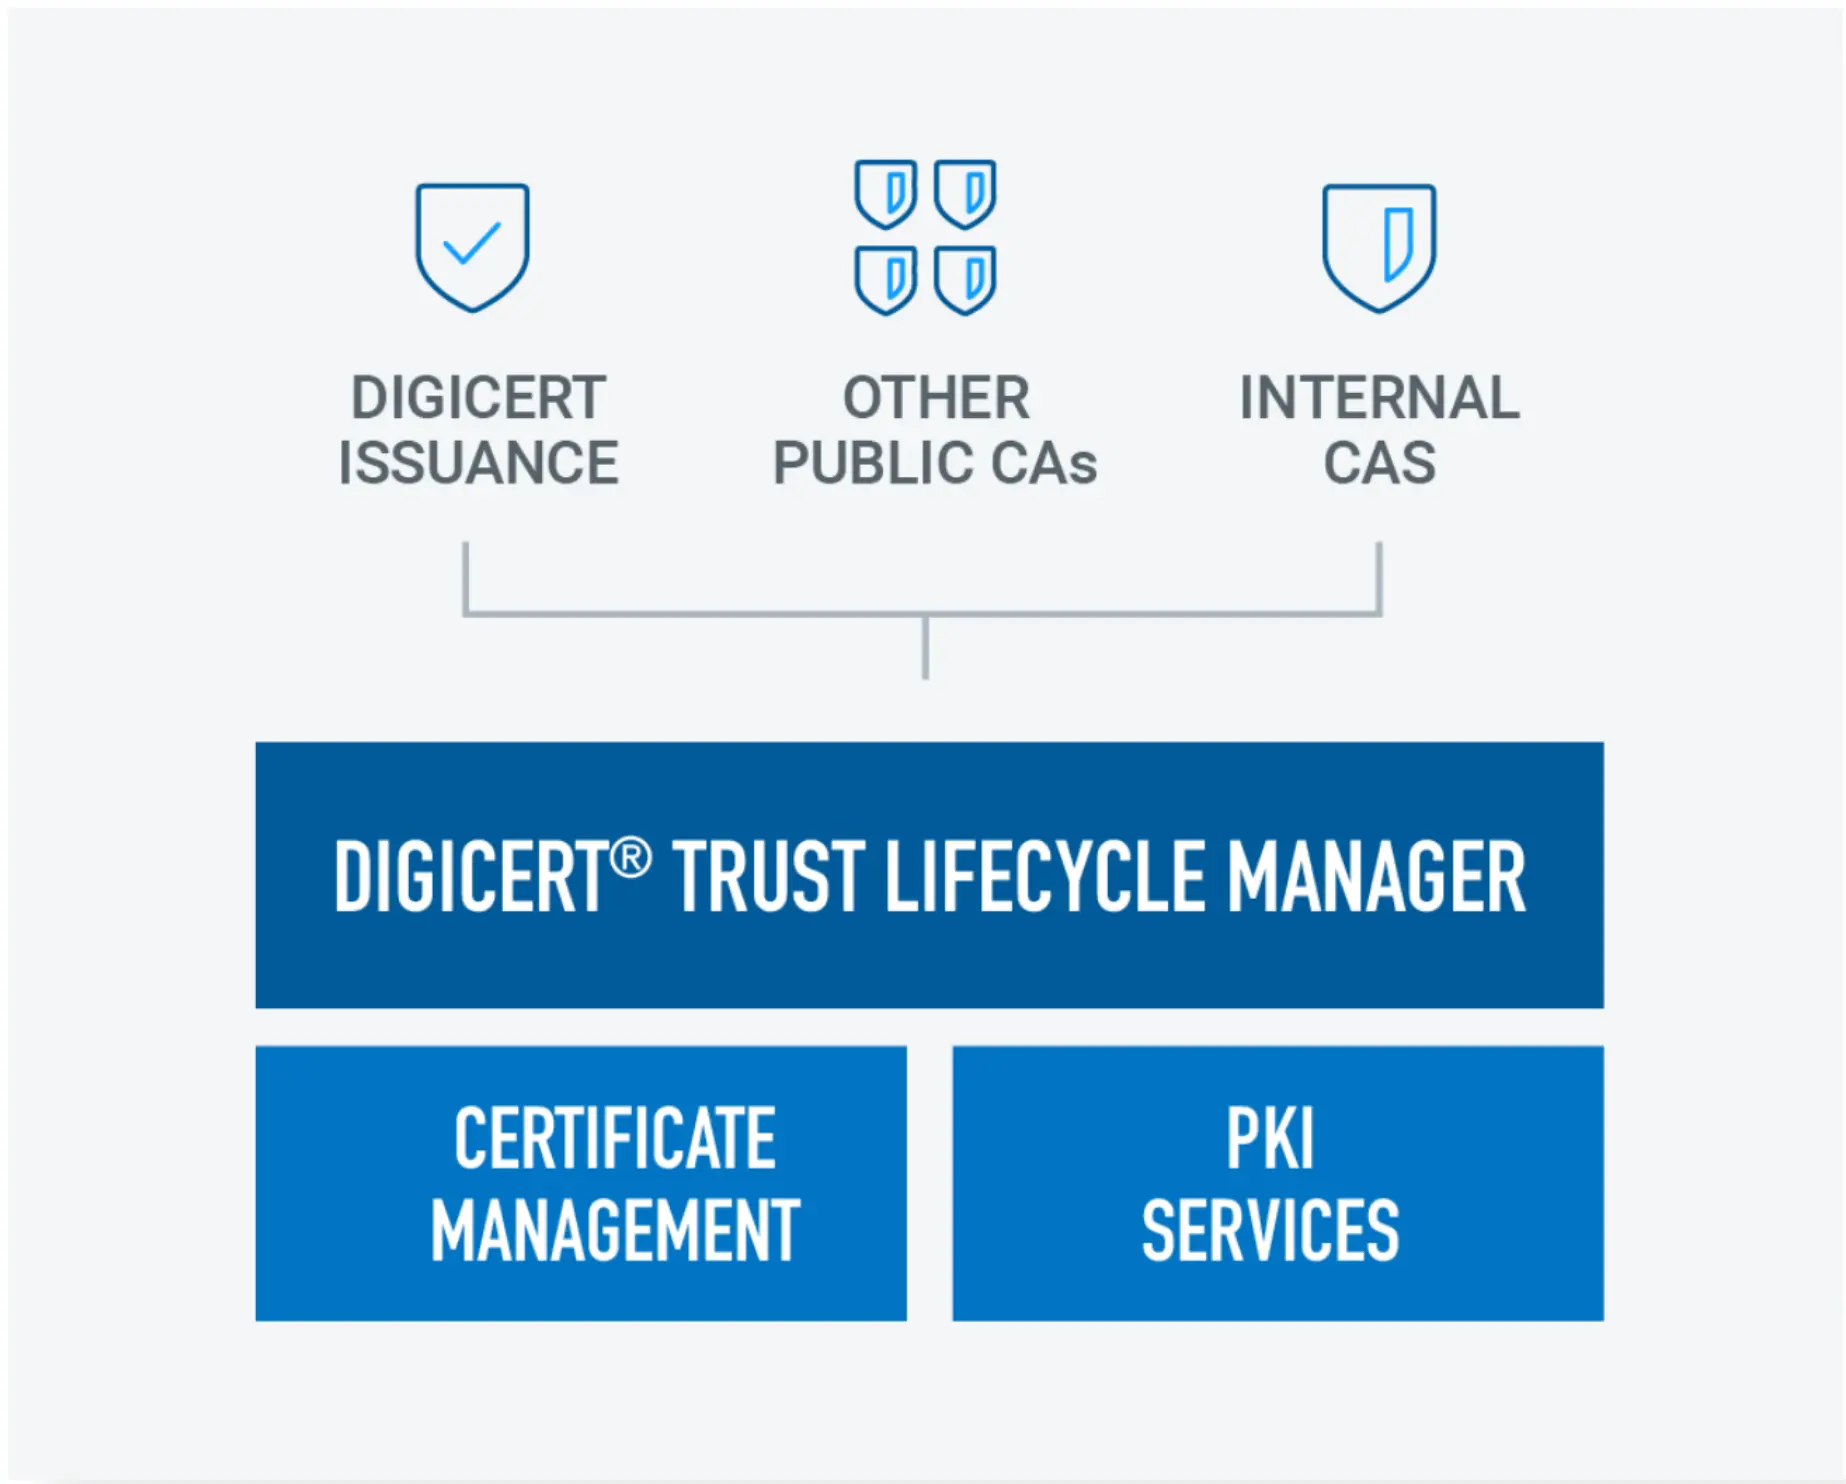
As the name suggests, this manager manages the entire certificate lifecycle. It's a certificate and PKI management tool that brings clarity and control to your organisation. With its help, you can automate certificate acquisition, renewal and installation, which you will then not have to worry about. It will not allow any certificates to expire without notice, causing problems or security risks.
Trust Lifecycle Manager allows you to apply the most common PKI usage methods in your organisation, such as:
- TLS/SSL certificates
- User and endpoint authentication
- Authentication of servers
- Secure email
- Intermediate Certificates (ICAs)
The certificate lifecycle automation, which is enabled by this DigiCert ONE component, can be used with the help of the ACME, Intune SCEP, EST and CMP protocols.
More information about Trust Lifecycle Manager can be found on the Trust Lifecycle Manager product page or in the Datasheet.
DigiCert Software Trust Manager
With Software Trust Manager, you can automate the signing of code developed in your company, confident that it will be trusted and secure to the world. Today, it is already standard to sign all applications, and Software Trust Manager can help you with this.
You can store the signature certificate in the DigiCert cloud, i.e. the HSM equivalent. Not only does the customer not have to purchase their own HSM; at the same time, it is the most secure way of signing. In addition, with Software Trust Manager, you can sign using the hash signing method, which is not only secure, but also extremely fast.
You can safely switch between the online/offline state of the keys and schedule their use, for example, only on the release of a new build. You can also allow only certain people access to the keys. This gives you a new level of signing security!
You can easily integrate this modern and secure signing into your current CI/CD. Software Trust Manager supports integration with every imaginable platform and, using PKCS11/KSP, offers integration with popular tools like Jenkins, Azure Pipelines, Gradle and more.
More information can be found on the Software Trust Manager product page or in the Datasheet.
SSLmarket is here for you
Arrange a non-binding consultation and demonstration of DigiCert ONE with us
I am interestedDigiCert Document Trust Manager
The exchange of documents over the Internet is not possible without an electronic signature, which ensures not only your identification, but also the integrity of the document and its immutability.
DigiCert Document Trust Manager provides a complete solution for managing digital certificates and document signing marks in the cloud. It can also be integrated with other signature solutions using the Cloud Signature Consortium (CSC) API.
This administrator supports AATL, eIDAS and ZertES certificates, which you can use directly in the DigiCert cloud and you do not have to sign documents offline using a certificate on a token. Certificates with this level of verification can serve as a substitute for a handwritten signature. You can also collaborate with multiple colleagues to sign and approve documents with DigiCert Document Trust Manager.
Part of the Document Trust Manager ecosystem is the management of certificate holders, their identities and verification, which takes place automatically and completely remotely. You no longer need to go to a notary to obtain signature certificates!
You can find more information on the Document Trust Manager product page or in the Datasheet.
DigiCert CertCentral TLS Manager
CertCentral TLS Manager is a manager of certificates and their lifecycle. With its help, you can not only obtain certificates, but also renew them. With advanced automation, you can request certificates directly from your servers using ACME or automation agents (API).
However, SSLmarket customers do not need CertCentral as they have the same (and better) features available in their SSLmarket account; the DigiCert solution does not offer them much extra (for example, apart from the function of inspecting certificates in the network).
More information can be found on the DigiCert CertCentral TLS Manager product page, or in the Datasheet.
DigiCert IoT Trust Manager
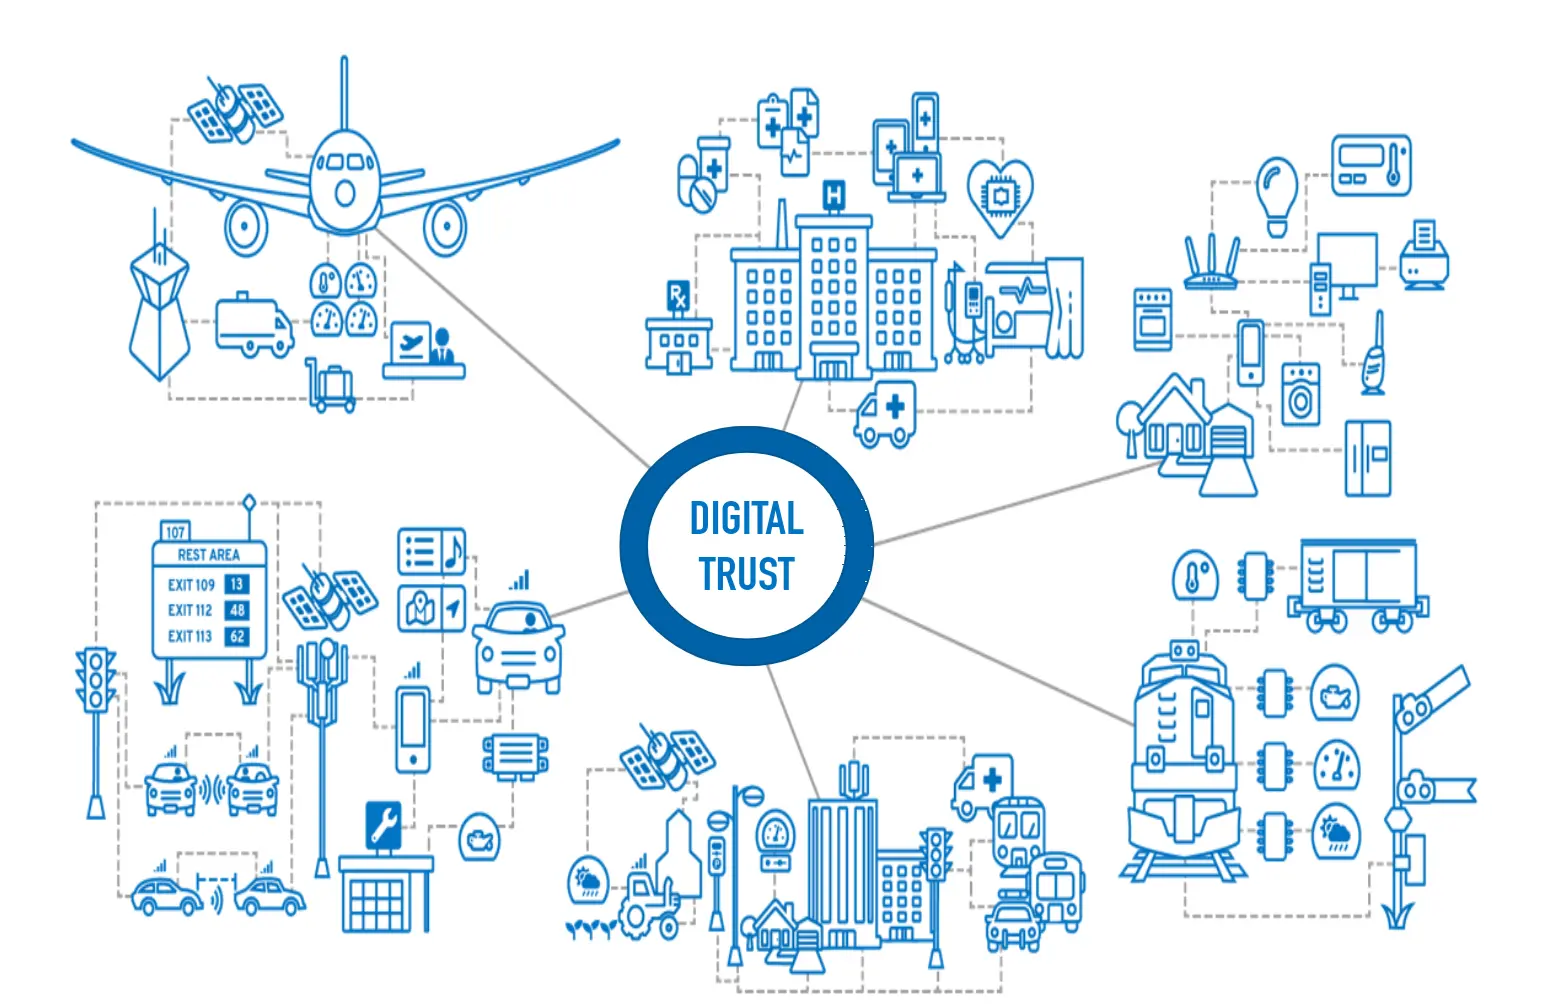
Do you manufacture or assemble hardware? Manage device identity at a large scale, at every stage of their lifecycle, with DigiCert IoT Trust Manager. It is a PKI management solution that embeds the identity in the device and manages it. It supports all types of certificates and keys used today (RSA, ECDSA, Edwards), a wide range of protocols for obtaining a certificate (EST, CMPv2, SCEP, ACME, REST API) and several options for authenticating their issuance. It authenticates and issues certificates in cooperation with other DC1 components.
It is suitable both for manufacturers of electronics, chipsets and similar components, as well as for equipment manufacturers who assemble them.
You can find more information on the IoT Trust Manager product page or in the Datasheet.
Integration with DigiCert ONE
All DC1 components offer a separate API, so you don't have to worry about connectivity. The API allows integration with any of your systems.
DigiCert strongly supports developers and software development where code signing is a must. It offers libraries for all operating systems and development platforms. With modern hash signing, you can sign using KSP on Windows, with CryptoTokenKit (CTK) on the Apple platform; thanks to PKCS11, hash signing supports Java, Android, Linux, Docker, OpenSSL, GPG, XML and more.
As you can see, integration with existing technology platforms is not a problem. DigiCert ONE is intended for modern companies that develop agilely using DevOps. It will greatly help you in CI/CD security.
How to get DigiCert ONE?
If you are interested in more information, demonstrations or independent pricing, do not hesitate to let us know and we will provide you with the necessary information. We will be happy to demonstrate the individual components of DigiCert ONE live.

ZONER a.s.
86-90 Paul Street
London EC2A 4NE
United Kingdom
VAT ID: CZ49437381
Invoice address: Nové Sady 18, 602 00 Brno